Critical PHP flaw: Ministry of Digital Transformation says government sites secured
Ministry of Digital Transformation says preventative blocks, patching and checks were applied and no signs of compromise were found so far.
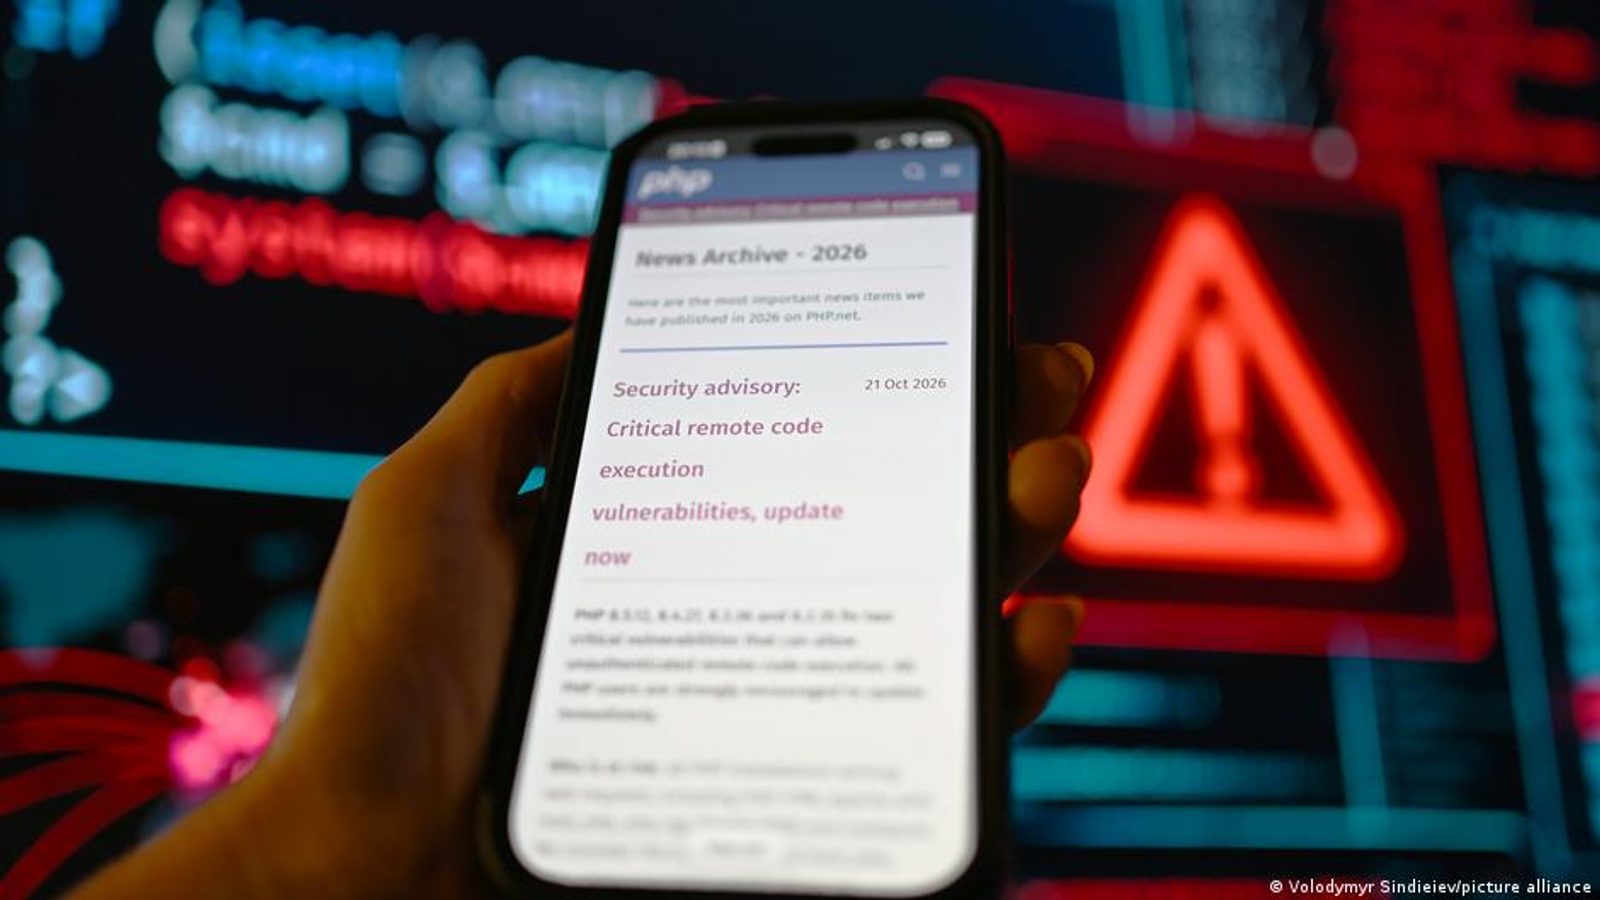
The Ministry of Digital Transformation said on October 22, 2026 that government websites were protected after global alerts about a critical PHP vulnerability prompted emergency checks and defensive measures.
According to the ministry, protective and technical steps were taken immediately after the vulnerability was disclosed to secure the web systems used by the Government and its ministries.
What the ministry says it did
“As part of preventive activities, external web traffic to the affected systems was temporarily blocked in order to prevent potential exploitation of the vulnerabilities. Then checks of software versions were carried out, appropriate security patches and updates were applied, and the functionality and security of the web services were checked,” the Ministry of Digital Transformation (MDT) said.
MDT added that measures focused on reducing the risk of unauthorized access, remote execution of malicious code and potential compromise of web servers. “According to the checks so far, there are no indications of successful exploitation of the mentioned vulnerabilities or of compromise of the Government's and ministries' websites,” the ministry said.
The national computer incident response team, MKD-CIRT, on October 21 warned about a critical PHP security flaw identified as CVE-2026-109618 (GHSA-w8hw-w9fx-j79w), which can allow remote code execution (RCE) without prior authentication. MKD-CIRT noted that the weakness stems from improper memory handling when available memory is exhausted and that specially crafted HTTP requests could trigger execution of malicious code under the web server account. A related critical issue, CVE-2026-109619, was removed in the same security releases.
MKD-CIRT urged administrators, hosting providers, institutions and companies to update PHP to the security releases immediately, inspect servers and PHP-based web applications, analyse security logs and apply temporary access limitations where updates cannot be installed right away. The ministry said MDT's cybersecurity sector and the government incident response team will continue heightened monitoring for indicators of compromise and further analysis of security events.
Photo: press material from the event